

ISO 27001:2022
ISO/IEC 27001:2022 – Information Security Management System (ISMS)
Protect Your Business Information with ISO 27001
ISO/IEC 27001:2022 is an internationally recognized standard that specifies requirements for establishing, implementing, maintaining, and continually improving an Information Security Management System (ISMS). It helps organizations protect sensitive information, manage security risks, and strengthen information security practices.
The standard is suitable for organizations of all sizes and across different industries. It provides a systematic approach to managing information security by addressing people, processes, technology, and organizational risks.
What Is an Information Security Management System (ISMS)?
An Information Security Management System (ISMS) is a structured framework of policies, procedures, processes, and controls designed to protect an organization's information assets.
An effective ISMS helps maintain three essential aspects of information security:
-
Confidentiality: Ensuring information is accessible only to authorized individuals.
-
Integrity: Maintaining the accuracy and completeness of information.
-
Availability: Ensuring information and systems are accessible when required.
ISO/IEC 27001 helps organizations identify information security risks, implement appropriate controls, monitor their effectiveness, and continually improve their security arrangements.
Key Steps in ISO 27001 Implementation
Implementing an ISMS involves a structured process tailored to the organization's activities, risks, and information security needs.
Key steps include:
-
Define the Information Security Policy: Establish the organization's commitment and approach to information security.
-
Determine the ISMS Scope: Identify the business functions, locations, systems, and information assets covered by the ISMS.
-
Conduct a Risk Assessment: Identify information security threats, vulnerabilities, and potential impacts.
-
Develop a Risk Treatment Plan: Determine how identified risks will be addressed.
-
Select Appropriate Security Controls: Choose controls based on risk assessments and applicable requirements.
-
Prepare the Statement of Applicability (SoA): Document the applicable controls, their implementation status, and justifications for inclusion or exclusion.
-
Monitor and Improve the ISMS: Conduct internal audits, management reviews, and ongoing performance evaluations.
Benefits of ISO 27001 Certification
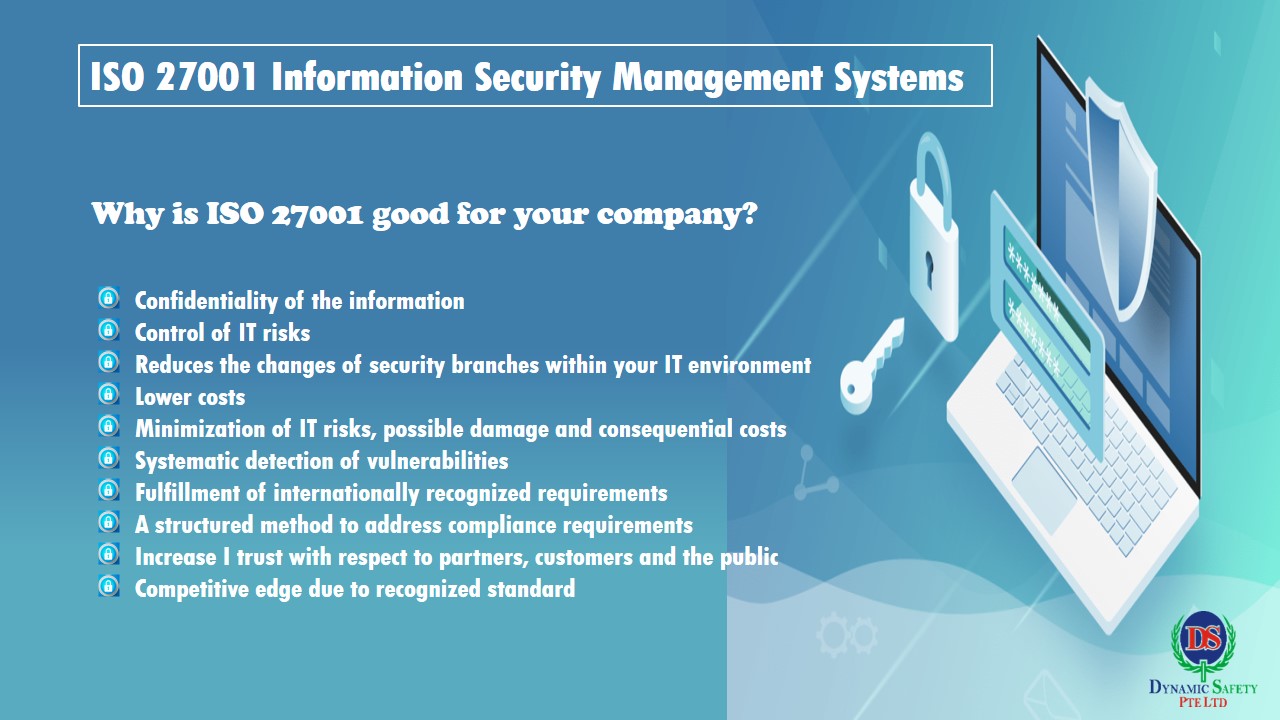
Implementing ISO 27001 can help organizations strengthen information security and improve confidence among customers, suppliers, and business partners.
Key benefits include:
-
Improved protection of confidential and sensitive information.
-
Systematic identification and management of information security risks.
-
Better preparedness for cyber threats and security incidents.
-
Improved customer and stakeholder confidence.
-
Support for meeting relevant contractual and regulatory obligations.
-
Stronger business resilience and operational continuity.
-
Clearer information security responsibilities and procedures.
-
Continual improvement of information security practices.
How Dynamic Safety Can Help You
Dynamic Safety provides consultancy support to help organizations develop and implement an Information Security Management System aligned with ISO/IEC 27001 requirements.
Our approach focuses on understanding your organization's information security needs, identifying gaps, and establishing practical processes to improve information protection.
Our support may include:
-
Gap Assessment: Review existing information security practices and identify areas requiring improvement.
-
ISMS Development: Support the establishment of information security policies, procedures, and processes.
-
Risk Assessment Support: Help identify and evaluate information security risks.
-
Documentation Assistance: Guide the preparation of relevant ISMS documents and records.
-
Implementation Guidance: Support the integration of information security controls into business operations.
-
Internal Audit Preparation: Help prepare for internal audits and management reviews.
-
Certification Audit Preparation: Support your organization in preparing for an independent certification assessment, where applicable.
Our services can be tailored to your organization's size, industry, information security risks, and business objectives.
Strengthen Your Information Security with Dynamic Safety
Protecting business information is essential for maintaining customer trust, managing risks, and supporting long-term business growth.
Contact Dynamic Safety to learn how ISO/IEC 27001 consultancy can help your organization establish a structured approach to information security management.